
What is @blockhertz_audit_bot?
Most smart contract audits cost thousands of dollars and take weeks. For developers who want a quick sanity check before a deployment — or security researchers scanning a suspicious address — that is overkill.
Today we are launching @blockhertz_audit_bot on Telegram: a free bot that runs a live AI security audit on any deployed smart contract and returns a risk score plus the most critical findings in under 30 seconds. No signup. No install. Just Telegram.
How it works
Open the bot, send one command, get results:
/audit 0xYourContractAddress
/audit 0xYourContractAddress base
The bot fetches the verified Solidity source from the block explorer, passes it through the Blockhertz AI Security engine, and returns a risk score from 0–100 plus the top critical and high-severity findings.
Step by step
1. Send the address — type /audit 0x... in the bot chat. Add a chain name after the address if it is not on Ethereum mainnet.
2. Source is fetched — the bot pulls the verified Solidity source from the chain's block explorer. Unverified contracts return a clear error.
3. AI analysis runs — the source is checked for reentrancy, access control issues, integer overflow, delegate call risks, and dozens of other vulnerability patterns.
4. Results delivered — you get a risk score, the top 1–2 critical and high findings, and a link to the full report.
Real example — Uniswap token on Ethereum
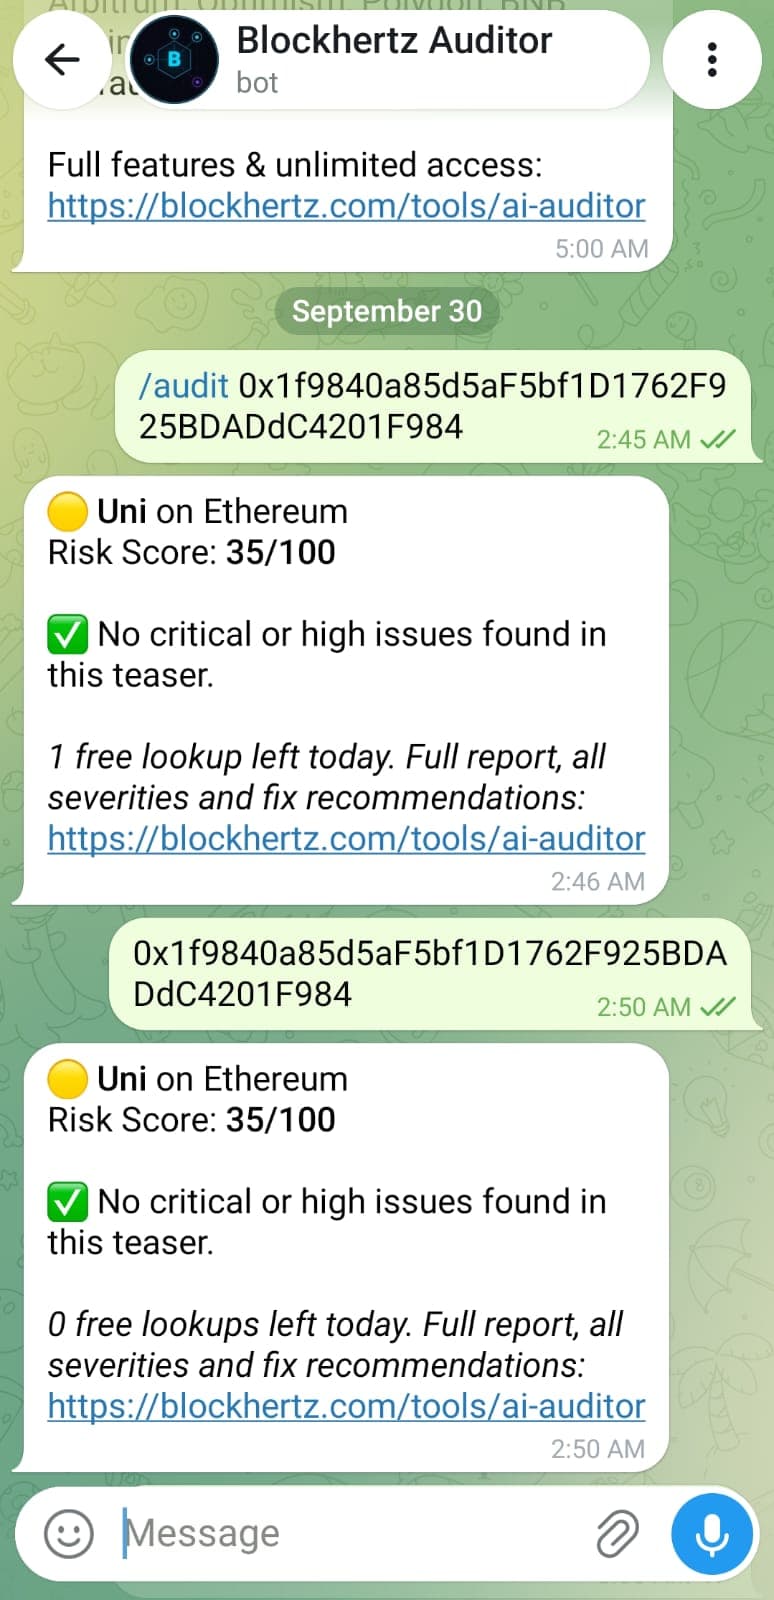
We audited 0x1f9840a85d5aF5bf1D1762F925BDADdC4201F984 (the UNI governance token) as a live test:
🟡 Uni on Ethereum
Risk Score: 35/100
✅ No critical or high issues found in this teaser.
1 free lookup left today. Full report, all severities and fix recommendations: https://blockhertz.com/tools/ai-auditor
Score 35 out of 100, no critical or high findings — exactly what you would expect from a battle-tested, widely-audited token contract. The bot also resolved the contract name from the verified source metadata automatically.
Risk score ranges at a glance:
| Score | Risk Level | Recommendation |
|---|---|---|
| 0–30 | Low | Looks clean, review recommended before mainnet |
| 31–60 | Moderate | Review findings before deployment |
| 61–85 | High | Professional audit strongly recommended |
| 86–100 | Critical | Do not deploy without a full audit |
Supported chains
The bot supports six chains. Use the chain name after the address:
| Chain | Command |
|---|---|
| Ethereum (default) | /audit 0x... |
| Base | /audit 0x... base |
| Arbitrum | /audit 0x... arbitrum |
| Optimism | /audit 0x... optimism |
| Polygon | /audit 0x... polygon |
| BNB Chain | /audit 0x... bnb |
Free tier vs full AI Auditor
The bot is free with no account required. Each Telegram user gets 2 audits per day, resetting at midnight UTC.
| Feature | Telegram Bot (free) | AI Auditor (full) |
|---|---|---|
| Risk score | ✓ | ✓ |
| Critical & high findings | Top 1–2 | All findings |
| Medium & low findings | — | ✓ |
| Gas optimizations | — | ✓ |
| Fix recommendations | — | ✓ with code examples |
| Daily limit | 2 audits | Unlimited (credit-based) |
| Signup required | No | Yes (free account) |
Also available as a Hardhat plugin
If you use Hardhat, you can integrate the same AI audit directly into your build pipeline with hardhat-blockhertz — now officially listed on Hardhat's community plugins page.
npm install hardhat-blockhertz

npx hardhat blockhertz-audit
npx hardhat blockhertz-audit --contract contracts/MyToken.sol
The plugin supports the same six chains, exclude patterns for test files, a failOn option for CI pipelines, and a credit-usage prompt before every run.
Why we built this
Existing security tools — Slither, MythX, Securify — require local setup, Python environments, and significant configuration before they return a result. That friction means many developers skip the check entirely, especially for quick experiments or third-party contracts they are about to interact with.
We wanted zero friction. No CLI, no API key, no wallet connection. Paste the address, get the answer. The bot is not a replacement for a professional audit before a mainnet launch — but it is a useful first filter that takes seconds instead of days.
Try it now: open Telegram and search @blockhertz_audit_bot, or use the full AI Auditor at blockhertz.com/tools/ai-auditor.
Related Articles
Blockchain Security Statistics 2026: Smart Contract Hacks, Losses and Trends
$3.4 billion stolen from blockchain projects in 2025. Access control failures cost $953 million. Audited contracts have 98% fewer hacks. Complete blockchain security statistics for 2026 — updated monthly by the Blockhertz team.
Read article →Smart Contract SecurityInteger Overflow in Solidity: What It Is, Real Examples, and How to Prevent It (2026)
Integer Overflow in Solidity: What It Is, Real Examples, and How to Prevent It (2026) An integer overflow vulnerability occurs when arithmetic operations exceed the maximum value a data type can hold...
Read article →Smart Contract SecurityBlockhertz vs Slither: Smart Contract Security Tool Comparison (2026)
Blockhertz AI Auditor and Slither are both free smart contract security tools — but they serve different purposes. This guide compares both to help you choose the rightone for your workflow.
Read article →Resource Hub
Smart Contract Security Hub →
Free AI auditor, vulnerability guides and security research
Explore Blockhertz
Views
7
Read Time
7 min read
Likes
0
Published
Sep 29, 2026
SIGNAL THREAD
NO SIGNALS YET — BE FIRST TO TRANSMIT
Muhammad Asif
Senior Blockchain Developer & Founder, Blockhertz
Blockchain developer and security engineer with 8+ years of experience. Founded Blockhertz in 2018 to build AI-powered tools for Web3 teams — smart contract auditing, architecture generation, gas optimization, and RWA tokenization platforms. Serving clients worldwide.